PHP2Shell: two critical PHP flaws (CVSS 9.2) force emergency patches for millions of websites
What happened
On October 21, the PHP security team released emergency patches for two critical remote-code-execution vulnerabilities — CVE-2026-109618 and CVE-2026-109619 — collectively nicknamed PHP2Shell. Both flaws score 9.2 out of 10 on the CVSS severity scale, and both let attackers run code on a server without logging in.
The fixes are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, according to BleepingComputer. The PHP project is blunt about the remedy: updating to a patched release is the only complete mitigation.
What is actually affected
This is the part that makes PHP2Shell unusually broad. The flaws sit inside the PHP language runtime itself — not in any app, plugin or theme — so they affect all PHP installations that serve web requests: PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed.
The PHP team considers Apache's mod_php the highest-risk setup, BleepingComputer reported. The reason: a demonstrated exploit fires from a single unauthenticated request before any application code runs — meaning even a perfectly written website cannot defend itself at the application layer.
PHP powers roughly 70% of websites worldwide, including WordPress, Drupal and Joomla, according to AlternativeTo. Researchers estimate around 1.3 million internet-connected hosts could be exposed.
How the flaws were found
The vulnerabilities were discovered by security researchers at Calif, OpenAI and Wiz, BleepingComputer reported. OpenAI noted that AI-assisted security research helped identify the flaws, develop working exploits and verify the patches as part of a coordinated disclosure — one of the first major vulnerabilities where AI did serious offensive-and-defensive work in the open.
Both bugs stem from the same underlying problem, the PHP team said: PHP can leave its memory in a corrupted state when a request ends abnormally. CVE-2026-109618 abuses out-of-memory corruption to run code with the web worker's privileges; CVE-2026-109619 exploits stale global state, enabling heap use-after-free, memory disclosure and remote code execution.
The vulnerable code dates back more than a decade, according to AlternativeTo.
Attacks are already happening
The disclosure has an ugly timing problem: details leaked before the patches landed. Cloudflare's CTO said the company observed early attacks at 07:43 UTC on October 21, security analyst Scott Harvanek reported. WatchTowr now lists CVE-2026-109619 as exploited in the wild. Sansec, which tracks e-commerce attacks, told Hadrian it expects mass exploitation now that both the patches and the write-ups are public — and that a circulating attack tool combines both flaws into one unauthenticated attack.
The reaction in Japan shows how seriously the industry is taking it. Ahead of the release, services including pixiv, DMM.com and niconico went into emergency maintenance, Japan Cyber Watch reported. The country's National Cyber Office said temporarily stopping websites is an effective way to reduce risk when patching quickly is difficult — and Prime Minister Sanae Takaichi repeated the call on X, describing it as an "urgent request".
A disagreement: how big is the exposure?
The exposure numbers depend on who counts and how. Security researcher Silas Cutler estimates over 1.3 million internet-exposed hosts are potentially vulnerable; a separate Shodan banner count by Henk Poley put 1.9 million hosts advertising PHP. These measure different things — banners versus assessed vulnerability — so the figures do not directly compare. gagariya recorded both without treating either as final.
What site owners should do now
- Patch first. Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 — matching your release line — then restart PHP-FPM, Apache or whichever service runs your PHP workers. Hadrian notes that old workers keep running the vulnerable code until restarted.
- Don't rely on temporary mitigations. PHP outlined interim measures for systems that cannot patch immediately, but says none of them fully blocks potential attacks. If a site cannot be patched, the project says consider taking it offline until it can.
- Check old versions. PHP 8.1 and older no longer get official updates. Some distributions and LTS vendors provide backported fixes — ask your vendor. PHP also published minimal source backports for 7.4, 8.0 and 8.1 for teams that build from source, BleepingComputer reported.
- Start with the riskiest hosts. Public-facing servers running Apache mod_php go first, since the demonstrated exploit needs no authentication at all.
Think of it like a broken lock on a building's main entrance: it doesn't matter how good the alarm in each flat is if anyone can walk through the front door.
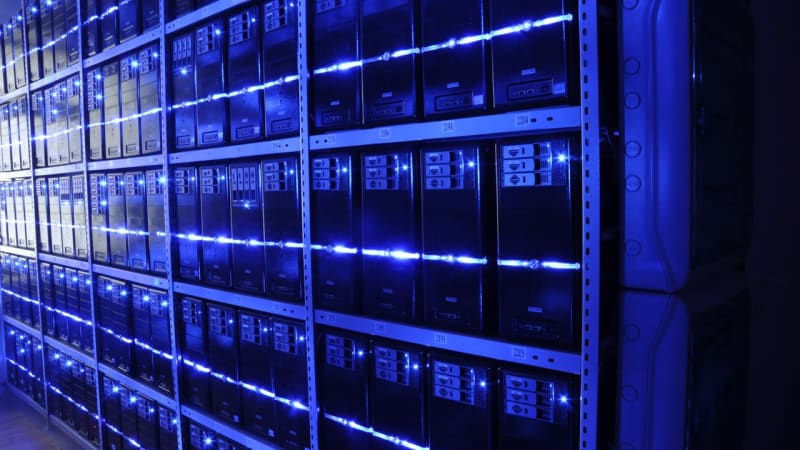
📷 Photo credit: BalticServers.com, Wikimedia Commons (CC BY-SA 3.0)
Questions people ask
- What is PHP2Shell?
- PHP2Shell is the collective name for two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, announced October 21, 2026. Both allow unauthenticated remote code execution on PHP servers and score 9.2 out of 10 in severity. They affect the PHP runtime itself, so every PHP setup serving web requests is potentially exposed.
- Is my website affected?
- If your site runs on PHP — including WordPress, Drupal, Joomla or any custom PHP app — treat it as exposed until patched. Check which PHP version your server runs; only 8.2 through 8.5 have official fixed releases (8.5.12, 8.4.27, 8.3.36, 8.2.35).
- What should I do right now?
- Update PHP to the fixed release for your version line, then restart the web service so old worker processes are replaced. Back up first and schedule a maintenance window. Do not rely on partial mitigations — the PHP security team says patching is the only complete fix.
- Why is mod_php considered the highest risk?
- Because the PHP team demonstrated an unauthenticated exploit against mod_php that triggers before any application code runs. That means your application's own security measures — app-layer firewalls, input validation — cannot stop it.
- My server runs PHP 7. What are my options?
- Migrate to a supported, fixed release. PHP 8.1 and older receive no official updates; some Linux distributions or LTS vendors ship backported fixes, and PHP published minimal source backports for 7.4, 8.0 and 8.1 for those who build from source.
Sources
- BleepingComputer: PHP ships emergency patches for critical PHP2Shell flaws (bleepingcomputer.com)
- AlternativeTo: PHP patches critical AI-discovered PHP2Shell vulnerabilities affecting millions of sites (alternativeto.net)
- Scott Harvanek: PHP2Shell follow-up — patches out, exploitation underway (scottharvanek.com)
- Hadrian: php2shell leaked critical PHP RCEs (hadrian.io)
- Japan Cyber Watch: PHP2Shell — patches, Japan services pause (japancyberwatch.com)
Editorial Note: This explainer was researched using verified primary sources and official notifications, then independently fact-checked, reviewed, and finalized under human editorial guidance by the Gagariya desk.
Keep reading
technology · 26 Oct 2026
21 publishers challenge DPDP Act in Supreme Court
The DNPA petition argues consent and erasure rules could affect investigations, sources and published reports. The matter is listed for 27 October 2026.
technology · 26 Oct 2026
फ़र्ज़ी सरकारी वेबसाइट कैसे पहचानें: पूरी जाँच गाइड
असली जैसा दिखने वाला पोर्टल भी नकली हो सकता है। लिंक खोलने से पहले डोमेन, हड़बड़ी वाले दावे और OTP की माँग को परखें।
technology · 25 Oct 2026
OnePlus 15 gets ColorOS 17 early in India
ColorOS 17 has reached the OnePlus 15 in India ahead of schedule, replacing OxygenOS 16. Here is the build number, the download size, what is new, and when other OnePlus phones get it.
The day’s verified stories, one email, 7 am IST. No noise.